- Agentforce
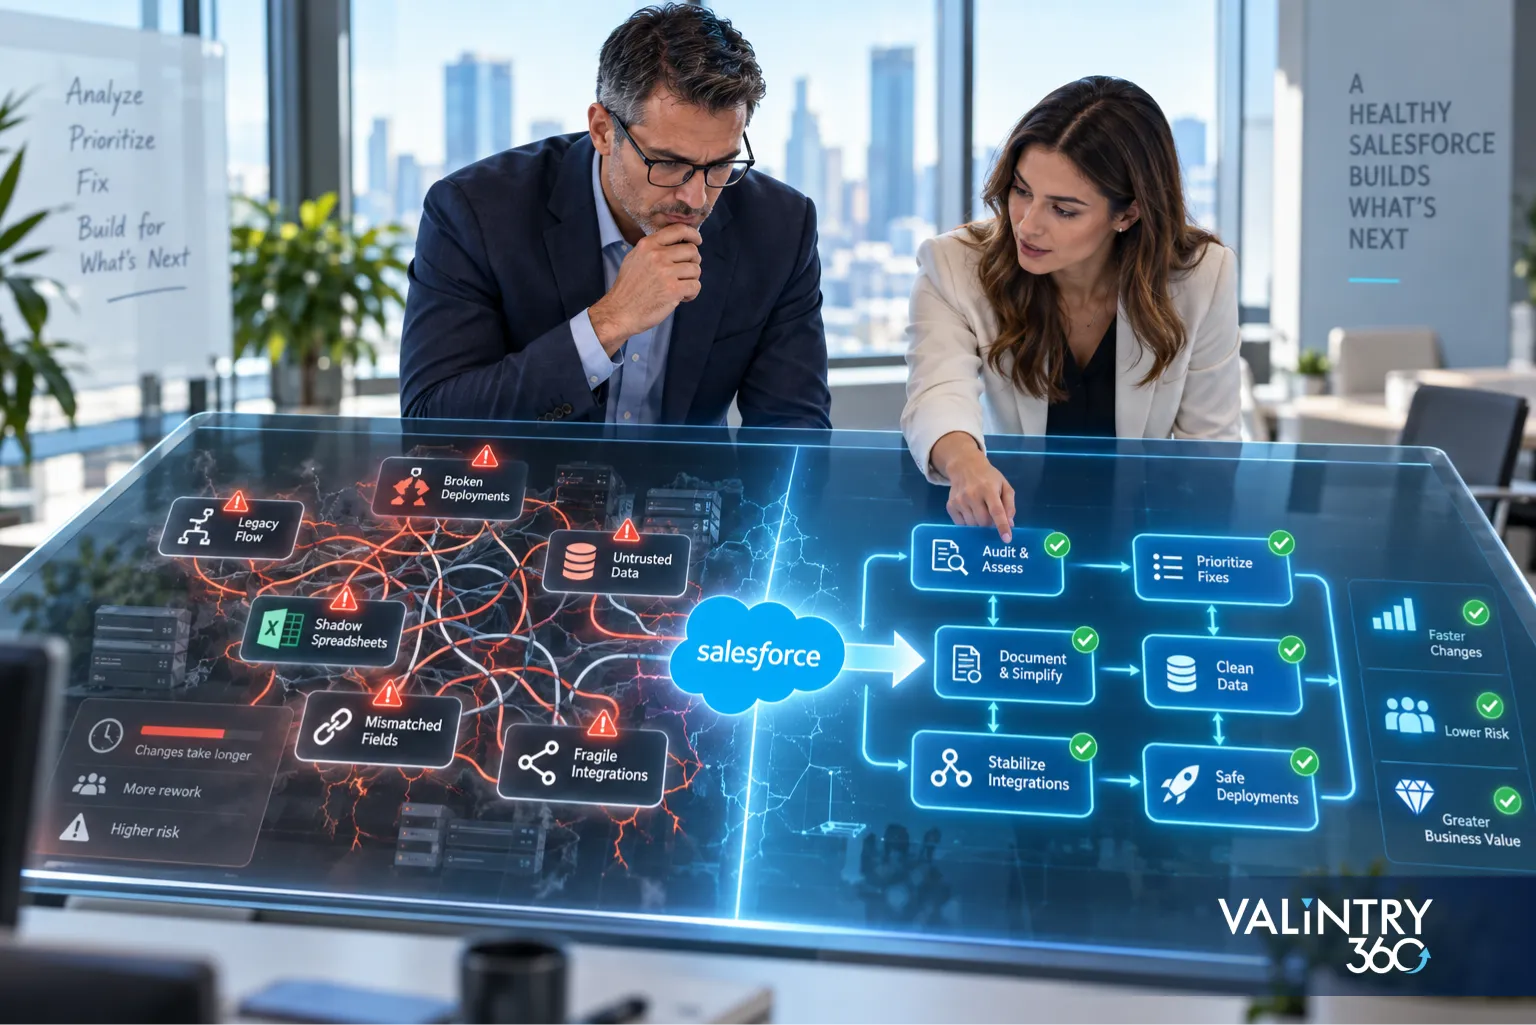
A small field change takes three days because nobody’s sure what it’ll break downstream. A deployment fails, gets patched, and fails again the next sprint. An old Flow keeps running untouched because nobody documented what it actually does. Somewhere in your org, a team is quietly maintaining a shadow spreadsheet because the CRM data can’t be trusted, and a sales rep has stopped logging activity in Salesforce altogether because the fields never matched what they actually needed to track.
None of that is bad luck. It’s Salesforce technical debt: the accumulated code, configuration, automation, data, and integration shortcuts that make every future change slower, riskier, and more expensive than it should be. Debt shows up as friction, a little more of it every quarter, until a routine sprint takes three times as long as it used to and every release meeting includes someone asking “what else does this touch?”
This guide covers four things: where technical debt actually hides across a Salesforce org, what it costs in hours and dollars you can calculate yourself, how to audit an org and rank what to fix first, and how to repair debt safely without breaking what already works.
What Salesforce Technical Debt Means
Salesforce technical debt is any technical choice, aging component, incomplete migration, or deferred maintenance task that increases the cost, effort, or risk of changing the org later. Salesforce’s own Well-Architected Framework frames it the same way: an architectural decision either holds up over time or it quietly becomes a liability.
It’s not automatically a mistake. Sometimes it’s a shortcut a team took on purpose to hit a launch date, meaning to clean it up later. The not-cleaning-up part is what turns a shortcut into debt. Salesforce’s own code-quality guidance agrees: debt belongs in a visible backlog with context, business impact, and a repair estimate.
How debt accumulates
Debt rarely comes from one bad decision. It builds up from a handful of ordinary ones, stacked over years:
- Deadline-driven shortcuts that never got revisited
- Repeated admin changes made without a change record
- Implementation decisions that made sense in 2019 and don’t anymore
- Staff turnover that took undocumented knowledge with it
- Acquisitions or org consolidations that merged two sets of habits
- One-off custom development built for a single request
- Cleanup that kept getting pushed to “next sprint”
The debt cycle
The pattern is consistent enough to draw as a simple loop: a shortcut gets taken, other components start depending on it, maintenance load grows around it, and the repair backlog gets bigger than the one shortcut that started it. Break the loop early and the fix takes an hour. Wait two years, and it needs a dependency map, a test plan, and a change window.
Where Technical Debt Accumulates Inside a Salesforce Org
Technical debt doesn’t confine itself to code. It spreads across the whole environment, and most orgs carry it in more than one place at once.
Debt area | Examples to inspect |
|---|---|
Data model and metadata | Unused fields, old objects, duplicate definitions, stale layouts |
Automation | Workflow Rules, Process Builder, overlapping Flows, unclear order of execution |
Apex and custom code | Hardcoded values, old API versions, weak tests, dead code |
Integrations | Point-to-point connections, old endpoints, weak monitoring, unused credentials |
Data | Duplicates, stale records, poor definitions, excessive volume |
Security and access | Old users, broad profiles, unused permissions, connected apps |
Releases and development | Direct production changes, manual deployment steps, weak source control |
Documentation | Missing architecture records, unknown ownership, undocumented business logic |
Some of these are easy to spot once you know to look. Three fields named Status__c, Status_2__c, and Status_Old__c on the same object is a data-model tell. A Flow and a leftover Process Builder both firing on the same record update is an automation tell. A SOQL query sitting inside a loop is a code tell that shows up the moment record volume climbs past what it did in testing.
An org with a clean data model and messy Apex still has a debt problem. So does an org with tight code and a permission structure nobody’s reviewed since 2021. Debt in one of these areas tends to hide debt in the others, which is part of why it accumulates for so long before anyone notices.
Warning Signs Your Salesforce Technical Debt Is Affecting Daily Work
You don’t need a formal audit to notice debt. You just need to know what to watch for.
Symptom | Possible debt behind it | Business effect |
|---|---|---|
Small changes need long investigation | Unknown dependencies | Slower delivery |
Releases fail repeatedly | Weak testing or deployment controls | Rework |
Users keep shadow spreadsheets | Data or workflow problems | Lower CRM use |
Admins avoid changing old automation | Undocumented logic | Growing backlog |
Batch jobs fail | Code or volume limits | Incident hours |
Reports disagree with each other | Field or definition problems | Decision delays |
New hires need weeks to get oriented | Weak documentation | Higher support load |
Agentforce work stalls | Data, permission, or automation uncertainty | Project delay |
These symptoms are a reason to investigate, not a reason to start deleting metadata or rewriting code on the spot. A field that looks unused might be feeding a report someone runs once a quarter; a Flow that looks redundant might be catching a specific edge case nothing else covers. Diagnose before you treat, the same way a mechanic listens to an engine before pulling parts off it.
Symptoms that cluster are a stronger signal than any one symptom alone. Admins avoiding old automation while reports disagree with each other usually share one root cause: nobody trusts the data enough to change the logic producing it. An org can also look clean on the surface, happy users, tidy interface, and still carry serious debt in integrations or security that no user-facing symptom would ever reveal.
What Salesforce Technical Debt Costs the Business
This section puts technical debt in hours and dollars instead of leaving it as a vague sense that things are slower than they should be.
Maintenance capacity
Salesforce’s own guidance on resource and cost optimization notes that maintenance can consume 60% to 80% of development capacity in a mature org. That’s a maintenance figure, not a technical-debt figure specifically: some of that capacity goes to routine, healthy upkeep that has nothing to do with debt. But when maintenance is eating most of a team’s time, technical debt is almost always a large part of why, because debt is what turns a 30-minute fix into a two-day investigation.
What to measure
Track these cost areas separately, then add them up:
Cost area | What it covers | Calculation method |
|---|---|---|
Change investigation | Time spent figuring out what old code or automation does before touching it | Extra investigation hours × loaded hourly cost |
Rework | Repeat work caused by fixes that broke something else because a dependency wasn’t visible | Repeat work hours × loaded hourly cost |
Incidents | Response to problems traceable to known debt | Debt-related incident hours × team cost |
Release overhead | Extra release hours caused by unclear dependencies | Extra release hours × releases per year |
User workarounds | Manual work users do because the system doesn’t do what it should | Time lost per user × affected users |
Admin maintenance | Support tickets tied to confusing or broken configuration | Debt ticket hours × loaded cost |
System waste | Unused tools, storage, or duplicate platforms | Verified waste, priced directly |
Add those together and you get a working formula: annual debt cost equals recurring debt labor, plus incident cost, plus release overhead, plus verified system waste.
What this doesn’t capture
Delayed work belongs in a separate estimate. Feature delivery slips because half a sprint goes to unplanned cleanup. Migrations get postponed because the current state is too fragile to touch. AI projects get deferred because the data underneath them isn’t trustworthy yet. Keep this opportunity cost apart from the hard numbers above. It matters just as much as the tracked costs, but it’s harder to price with confidence, so mixing the two makes the whole calculation easier for a skeptic to wave off.
What Changed for Salesforce Technical Debt in 2026
A few developments this year changed what “current” technical debt management looks like on the platform.
Current finding | Why it matters |
|---|---|
Workflow Rules and Process Builder support ended December 31, 2025 | Legacy automation needs an owned migration plan with a firm deadline |
Salesforce’s architecture guidance recommends visible debt backlogs | Debt needs business context, an owner, and an effort estimate before it goes in the backlog |
Salesforce is connecting old metadata and governance gaps to AI readiness | Org cleanup now affects whether Agentforce work is even viable |
Code Analyzer v5 is the current supported generation | Static analysis can be part of both the audit and the release process |
Runtime and metadata signals together inform org-health decisions | Repair priority shouldn’t rely on a field count alone |
The Code Analyzer and runtime-signal points matter especially for teams still triaging debt by gut feeling instead of evidence. For orgs running mature implementations, this is the first year several of these land at once: an automation deadline that’s already passed, an audit tool that’s matured enough to lean on, and an AI program that depends on cleanup happening first rather than in parallel.
Taken together, these five changes point to the same shift: Salesforce is treating technical debt as a normal line item in architecture reviews now, not a problem developers quietly apologize for after the fact.
How to Run a Salesforce Technical Debt Audit
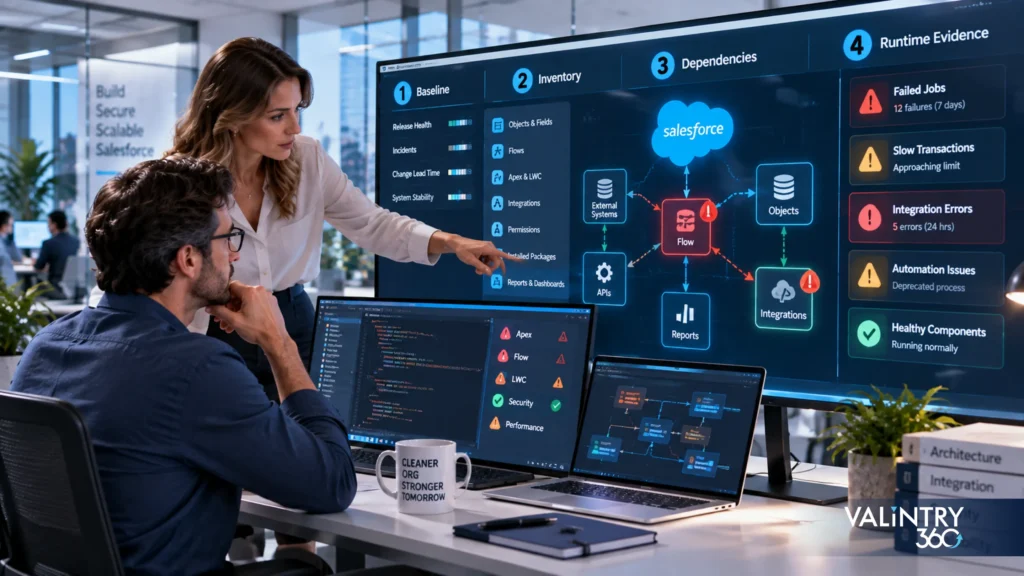
A real audit is a structured look at what exists, what depends on it, and what it’s actually costing you, not a full rebuild wearing a different label.
Step 1: establish a baseline
Before touching anything, record where things stand today: release failure rate, incident history, average change lead time, the themes showing up in support tickets, how many automations are in play, current integrations, and any open platform issues. Without a baseline, you can’t prove the audit made anything better.
Step 2: inventory the org
Go through it systematically: objects and fields, Flows, remaining Workflow Rules and Process Builder processes, Apex and Lightning components, API versions in use, integrations, permission structures, installed packages, data volumes, reports and dashboards, and whatever documentation exists. Salesforce’s own Code Analyzer can scan Apex, Visualforce, Flow, and Lightning components directly and flag security, performance, and coding-rule problems, which automates part of this step instead of leaving it to manual review.
Step 3: map dependencies
Before anyone changes a high-risk component, find out what relies on it: other Flows, Apex classes, integrations, and reports. This step alone prevents most of the self-inflicted incidents that come out of well-meaning cleanup work.
Step 4: check runtime evidence
Metadata tells you what exists. Runtime evidence tells you what’s actually a problem: errors, failed jobs, components approaching governor limits, slow transactions, and integration failures. A field with zero errors attached to it is a much lower priority than a Flow that fails once a week, even if the field looks messier on paper.
Step 5: build the debt register
Every finding should land in a register with the same fields, so nothing gets tracked informally and then forgotten:
Field | Purpose |
|---|---|
Debt item | What was found |
Domain | Code, automation, data, integration, and so on |
Dependency | What relies on it |
Business effect | Operational consequence |
Failure history | Known incidents |
Change frequency | How often the area gets touched |
Repair effort | Estimated work |
Owner | Responsible person |
Decision | Repair, retire, refactor, replace, or accept |
This mirrors the structure a Salesforce consulting review typically follows: baseline, inventory, dependencies, evidence, and a register, in that order, so nothing gets skipped or tracked informally.
How to Prioritize Salesforce Technical Debt
Not every finding deserves the same urgency, and treating them as equal is how audits turn into 300-item backlogs nobody ever works through.
Score each item
Rate every debt item from 1 to 5 on five dimensions: business impact, failure frequency, change frequency, dependency reach, and security or compliance exposure. Keep repair effort as a separate number rather than folding it into the score. You want to know both how bad something is and how hard it is to fix, and those two things don’t always move together.
A high-impact item with low repair effort is the easiest call you’ll make all quarter: fix it now. A high-impact item with high repair effort is the one that needs a named owner and a spot on the roadmap, because it’s not going away on its own and it’s not getting cheaper by waiting. Low-impact, high-effort items are usually the ones worth accepting rather than chasing.
The priority matrix
Priority | Typical condition | Action |
|---|---|---|
P1 | Active failure or high business exposure | Schedule immediately |
P2 | High dependency reach or rising repair cost | Put into the near-term roadmap |
P3 | Moderate effect with a manageable workaround | Repair alongside related work |
P4 | Stable and low-impact | Monitor |
Accepted | Current repair cost exceeds verified exposure | Assign an owner and a review date |
Issue count alone is a poor way to prioritize. A backlog with 300 low-impact metadata items can genuinely be less urgent than one failing integration that blocks order processing. Score by effect, not by volume.
Retire, Repair, Refactor, Replace, or Accept the Debt?
Every debt item eventually needs one of five decisions, and “fix it” isn’t specific enough to act on.
Treatment | Best fit |
|---|---|
Retire | Component has no remaining business use |
Repair | Problem is contained and the current design still fits |
Refactor | Function still matters, but the structure causes repeated maintenance |
Replace | A supported platform pattern or newer architecture is the better long-term path |
Accept temporarily | Exposure is known and current repair economics don’t justify action |
Replace is its own category because it usually means standing up something new rather than patching something old, closer in scope to a Salesforce implementation services engagement than a quick fix.
Questions to ask before choosing
How often does the component get changed? What depends on it? Has it caused production failures? Is the underlying technology still supported? Can its current behavior actually be tested? What would removing it affect? What does another year of maintaining it cost? And is another project already touching the same area, in which case the timing might solve itself?
A custom object built in 2020 for a promotion that ended in 2021, with no dependencies and no queries in a year, is a retire, not a debate. An Apex trigger that changes every quarter, feeds three integrations, and caused two incidents this year is a refactor candidate, not something to accept and revisit later.
A full rebuild is its own decision, and a bigger one. It should only follow real architecture, dependency, data, and business-process analysis, since replacing something carries its own migration and testing cost. At that scale, it functions more like a digital transformation engagement than a repair project.
How to Fix Salesforce Technical Debt by Domain
Salesforce technical debt remediation covers six different kinds of work, and treating them the same way wastes effort. A permission review and an Apex refactor need different people, different tools, and different testing.
Data model and metadata
Review actual usage, check dependencies first, retire fields and objects that have none, and clean up naming and descriptions so the next person doesn’t have to guess what something does. Much of this overlaps with ordinary Salesforce customization services work: renaming, consolidating, and retiring configuration rather than writing new code.
Automation
Build a real inventory of what’s running, understand the order of execution, merge duplicate logic, tighten error handling, consolidate Flows where it genuinely simplifies things, and cover the result with regression tests. Watch especially for Flows built to patch a problem in another Flow. That layering is one of the fastest ways automation debt compounds.
Apex and custom code
Run static analysis, remove hardcoded references, check bulk behavior against governor limits, raise test quality instead of just test coverage, retire calls to old API versions, and delete dead code rather than commenting it out. This is core Salesforce development services territory, the same skill set that built the org in the first place, aimed backward at what it already built.
Integration debt
Assign clear ownership to every integration, improve error handling, manage the lifecycle of each endpoint, rotate and track credentials, add monitoring where there’s none, and reduce point-to-point dependencies where a more central pattern would hold up better. This is Salesforce integration services work regardless of whether the connection in question is a marketing platform, a data warehouse, or an ERP integration with Salesforce: all three age the same way once nobody owns them.
Data debt
Deduplicate records, archive or remove stale ones, apply an actual retention policy, watch for record-volume problems before they hit limits, and get definitions consistent across objects that describe the same thing differently. Two objects both tracking “customer status” with different picklist values is a small problem in year one and a reporting nightmare by year three, which is where Salesforce data migration services work earns its keep: cleaning up what’s already there rather than moving new data in.
Security and access debt
Remove old users, tighten broad profiles, clean up permission sets, review connected apps, revoke privileged access that’s outlived its reason, and retire unused credentials. Access debt is the domain most likely to get skipped during a technical cleanup, and it’s also the one with the highest compliance exposure if it’s ignored.
Move Workflow Rules and Process Builder to a Supported Path
Salesforce support for Workflow Rules and Process Builder ended on December 31, 2025. Existing automation built on them can still run. What’s gone is the support and bug fixes behind them, which means any problem that shows up from here on is yours to solve without Salesforce’s help.
The migration sequence
- Inventory every active Workflow Rule and process.
- Identify scheduled actions and dependencies tied to each one.
- Document current behavior before converting anything.
- Identify which processes are good migration candidates.
- Convert supported patterns using Salesforce’s Migrate to Flow tool.
- Review the conversion results line by line.
- Test the converted Flow in a sandbox.
- Run regression tests against related processes.
- Activate the replacement automation.
- Deactivate the old Workflow Rule or process.
- Monitor production behavior after the switch.
Automated conversion doesn’t remove the need for a human to review the result. Patterns involving external callouts, Post to Chatter actions, Quick Actions, Submit for Approval steps, or recursive logic need redesign rather than a straight one-to-one conversion, and three overlapping processes that have quietly duplicated each other’s work for years are usually better merged into one Flow than converted side by side.
Treat this as a debt-repair project in its own right, not a background maintenance task. It has its own inventory, its own dependency risk, and its own testing requirements, the same as any other item in the debt register above.
Repair Debt Safely With Testing, Source Control, and Controlled Releases
Fixing technical debt without safeguards trades one kind of risk for another. Teams that skip this sequence to move faster usually end up slower, because an untested fix that breaks something else costs more time than the debt did in the first place.
Before repair: map dependencies, record current behavior, establish baseline tests, and define what “done” actually looks like. Skipping this step is how a routine cleanup turns into an incident report.
During repair: work in source control, get a peer review, run static analysis, update automated tests, and write down the architecture decisions made and why, so this fix doesn’t become next year’s undocumented debt.
Before deployment: run regression tests, review the security impact, rehearse complex releases before doing them for real, prepare a rollback plan, and confirm monitoring is actually watching the right thing.
After deployment: review any errors that came up, check performance against the baseline recorded earlier, verify the business behavior is what was intended, update the documentation, and close or revise the debt record.
Salesforce’s own DevOps Center source-control guidance treats source control as the single source of truth for a project’s changes, with a history of who changed what and why. That kind of traceability is what turns a completed repair into something provable rather than something someone remembers doing, and it’s the difference between closing a debt-register item with confidence and closing it because enough time has passed that nobody’s asking about it anymore.
How Technical Debt Affects Agentforce and Salesforce AI Work
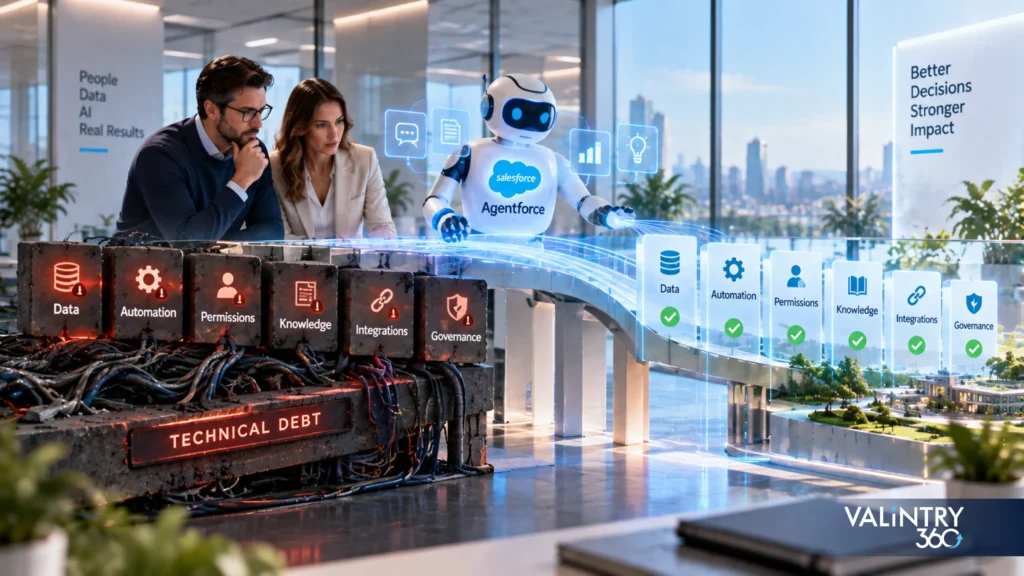
Salesforce’s own Center of Excellence AI governance guidance makes this explicit now: accumulated org debt now shapes AI readiness as directly as it shapes maintenance cost. An agent doesn’t know a field is stale or that a Flow’s logic is three overlapping patches deep. It acts on whatever it’s given, with the same confidence either way.
Data. Are the fields an agent would read current, meaningful, documented, and owned by someone who’d notice if they went stale?
Automation. Do you actually know what happens when an agent triggers an action or updates a record, or is that behavior buried in a Flow nobody’s looked at in years?
Permissions. What can users, agents, and connected services each access, and has anyone checked that on purpose recently?
Knowledge and business rules. If two systems define “active customer” differently, which one is the agent supposed to trust?
Integrations. Do the external actions an agent might call have clear ownership, real error handling, and monitoring that would catch a silent failure?
Governance. Who approves changes to prompts, agent actions, Flows, data access, and permissions once an agent is live?
This is the practical link between the two halves of this guide’s title: Salesforce AI solutions and Agentforce projects inherit whatever data and logic debt already exists in an org, which is exactly what the audit and remediation steps above are meant to clean up before an agent ever goes live. An org that’s run through the priority matrix and repaired its P1 and P2 items is starting an AI project from a materially different position than one that hasn’t.
Build Salesforce Technical Debt Management Into Normal Governance
Keeping technical debt under control is an ongoing governance habit, not a one-time cleanup project.
A governance calendar
Cadence | Review |
|---|---|
Every sprint | New debt created, repaired, or accepted |
Monthly | P1 and P2 debt, incidents, blocked work |
Quarterly | Org-health review and dependency checks |
Before major releases | Affected customizations and integrations |
Before major projects | Architecture and debt assessment |
Annually | Old packages, APIs, access, automation, and documentation |
Assign ownership
This needs a named owner who acts on findings rather than a committee that reviews them in passing: a Salesforce platform owner, an architect, an admin lead, a development lead, a security owner, and a business-process owner who can weigh in on what the org actually needs.
Track measures that mean something
Change lead time, deployment failure rate, incident hours, debt backlog by priority, the share of sprint capacity spent on debt, unsupported automation count, and regression failures. Salesforce’s own operational excellence guidance makes a fair point here: teams spending all their capacity on new features have no room left for the operational work that keeps debt from piling back up. Ongoing Salesforce managed services engagements typically fold this calendar into their standard cadence, and lighter-touch Salesforce managed support services can carry just the review calendar forward without a full engagement.
A related, narrower topic is prevention specifically, covered separately in best practices partners use to prevent technical debt and security issues.
Related Salesforce Case Studies
These five VALiNTRY360 case studies show the cost-and-fix side of this guide applied to real Salesforce orgs: legacy-system replacement, data consolidation, and process cleanup rather than net-new builds.
Case study | What it covers |
|---|---|
Replacing a legacy CRM and automating reconciliation work that used to eat a full work-month a year | |
Retiring an aging system outright rather than integrating around it, the same retire-versus-patch decision covered above | |
Consolidating sales and service data that had drifted apart across separate systems | |
How a Salesforce Marketing Cloud Implementation Helped BIC Graphic Cut Its Sales Cycle by 44% | Rebuilding marketing automation on a cleaner data foundation instead of layering more campaigns onto the old one |
Restructuring data architecture and automation workflows instead of accepting the org’s existing limits |
Each of these started with the same basic move this guide walks through: find out what’s actually there, decide what to keep, retire, or replace, and only then start building. None of the five began as a greenfield project; all five began by dealing with something that already existed and wasn’t working the way it should.
FAQs About Salesforce Technical Debt
1. What is Salesforce technical debt?
It’s the accumulated cost of technical shortcuts, aging components, and deferred maintenance across code, configuration, automation, data, and integrations. Each one makes future changes slower, riskier, and more expensive until it’s identified, prioritized, and addressed through an actual repair decision.
2. What causes technical debt in Salesforce?
Deadline-driven shortcuts, repeated ad hoc admin changes, aging implementation decisions, staff turnover, incomplete migrations, org consolidations after acquisitions, and maintenance that keeps getting deferred all contribute over time. It’s rarely one bad decision. It’s a dozen reasonable ones nobody circled back on.
3. How do I know if my Salesforce org has technical debt?
Watch for repeated deployment failures, small changes that take unusually long, overlapping automation nobody wants to touch, thin documentation, a rising volume of support tickets, and users building manual workarounds. Any one of these deserves attention; two or three together are worth a full audit.
4. How much does Salesforce technical debt cost?
It varies by org, so a universal figure isn’t reliable. Calculate it instead: add investigation hours, rework, incident response, release overhead, and admin maintenance, each multiplied by loaded hourly cost, then track delayed projects separately as opportunity cost.
5. What is a Salesforce technical debt audit?
A structured review combining a metadata inventory, dependency mapping, runtime evidence like errors and failed jobs, and business-cost data. It ends with a debt register that assigns an owner and a decision, retire, repair, or accept, to every finding.
6. How often should Salesforce org health be reviewed?
Quarterly reviews catch most drift before it becomes a real problem. Add targeted reviews before major releases and before large projects, plus one full annual pass across packages, APIs, access, automation, and documentation.
7. Which Salesforce technical debt should be fixed first?
Prioritize by business impact, failure frequency, dependency reach, and security or compliance exposure. A single integration failure that blocks order processing usually matters more than a long list of cosmetic metadata issues, so weigh effect before volume.
8. Should unused Salesforce fields always be deleted?
Not automatically. Check dependencies first: reports, integrations, and automation sometimes rely on fields that look unused. Confirm nothing references a field before retiring it, and document retention needs, since compliance or historical reporting can require keeping it anyway.
9. How do Workflow Rules and Process Builder affect technical debt in 2026?
Salesforce support for both ended December 31, 2025. Existing automation still runs, but with no fixes or bug support coming from Salesforce, so any problem that shows up now is yours to solve. A migration plan to Flow Builder is a real priority, not a someday task.
10. Can Salesforce Flow create technical debt?
Yes. Oversized Flows, duplicated logic across multiple Flows, weak error handling, and missing documentation create the same maintenance burden as any other automation debt. Flow being the current, supported tool doesn’t make it immune to the shortcuts that built up debt in Process Builder.
11. How does technical debt affect Salesforce releases?
Unclear dependencies raise the testing burden, increase deployment risk, and lengthen rollback planning. Releases that should be routine start needing extra rehearsal time just to feel safe, which slows down every team waiting on that release, not only the one that created the debt.
12. Can technical debt affect Agentforce projects?
Yes. Agents depend on current data, clear permissions, predictable automation behavior, and well-defined business rules. Debt in any of those areas undermines an agent’s reliability before it ever goes live, the same way it already undermines a human user’s trust in the data.
13. Should Salesforce technical debt be repaired during feature work?
Often, yes, when the debt sits directly in the area already being touched. It’s usually more efficient than a separate cleanup project later, as long as the related repair is planned and tested on its own, not squeezed in informally at the last minute.
14. When should a Salesforce org be refactored instead of rebuilt?
Refactor when the underlying architecture still fits the business and the debt is contained to specific components. Consider a rebuild only after comparing migration effort, dependency risk, and business fit against what a targeted refactor would actually cost to complete.
15. How can companies prevent Salesforce technical debt from returning?
Keep a visible debt backlog, require source control and testing for every change, document architecture decisions as they happen, review org health on a set cadence, and assign real ownership, since unclaimed debt is what accumulates fastest of all.
Related Posts
- Agentforce
Salesforce Consulting vs Implementation vs Managed Services
A company calls a firm and asks for "Salesforce consulting," expecting the team to configure the platform and go live in 6 weeks. Another buys an implementation and assumes the same people will keep fixing things a year later. A…
- Agentforce
Salesforce Dreamforce 2026: Your Complete Guide to Everything…
Salesforce Dreamforce 2026 wrapped up on September 17 at Moscone Center in San Francisco, and here is the one-line summary: this was the year Salesforce told the world its own user interface is optional. The headline announcement was AIforce, a…
- Agentforce
Agentforce Conversation Cost: What Counts as a Conversation…
Salesforce publishes one number for Agentforce and it looks settled. $2 per Conversation. Your actual Agentforce conversation cost depends on something that price tag never tells you, which is what triggers the charge in the first place.And that changes by…