- Salesforce Org Optimization & Technical
Salesforce is one of the most powerful growth platforms available to modern enterprises—but unmanaged, it can quietly turn into a maze of conflicting automations, redundant data, and mounting security exposure. Most technical debt and vulnerabilities stem not from bad intent, but from speed without structure.
Mature Salesforce Consulting and Solutions partners approach implementation differently. They use architectural discipline, security governance, and release controls that prevent these issues before they surface. By treating Salesforce as enterprise infrastructure—not just a CRM—organizations preserve agility while protecting data, compliance, and cost predictability.
Overview
- Designing Scalable Architectures That Eliminate Rework Before It Starts
- Embedding Security and Compliance From the Ground Up
- Governed Release Management: The Core of Debt Prevention
- Continuous Org Health and Optimization as a Business Discipline
- Translating Governance Into Real Business Value
- Conclusion
Designing Scalable Architectures That Eliminate Rework Before It Starts
Technical debt often begins with well-meaning teams trying to solve problems fast. Over-customization, quick fixes, or untracked integrations can seem efficient in the moment but lead to brittle systems that resist future change.
Experienced Salesforce Consulting and Solutions partners design for scale from Day 1. They focus on:
- Reusable architecture patterns that align with Salesforce’s roadmap and native capabilities.
- Documented data models that ensure consistency across clouds and integrations.
- Guardrails against over-customization, using configuration over code where possible.
- Component reusability, so enhancements don’t create ripple effects of rework.
By balancing innovation with governance, organizations avoid “org sprawl”—the slow buildup of unmanaged flows, scripts, and integrations that drive up maintenance costs. Scalable architecture isn’t about building slower; it’s about building once and expanding safely.
Embedding Security and Compliance From the Ground Up
Security is not a layer to bolt on after go-live—it’s an operating principle baked into every configuration and workflow. Mature Salesforce partners build least-privilege access, auditability, and compliance alignment into the foundation of every org.
VALiNTRY360’s Salesforce Consulting and Solutions team emphasizes measures like:
- Role-based access control (RBAC) that limits exposure while maintaining usability.
- Field-level security and data classification aligned with privacy frameworks such as SOC 2, HIPAA, or GDPR.
- Audit logs and event monitoring that enable traceability for compliance reviews.
- Data residency and retention policies that match corporate governance and regulatory needs.
These safeguards prevent unnecessary data exposure while maintaining flexibility for business growth. Instead of retrofitting controls after an audit finding, leading partners make compliance an everyday operating norm. That approach reduces remediation cost and improves executive confidence in Salesforce as a secure enterprise asset.
Governed Release Management: The Core of Debt Prevention
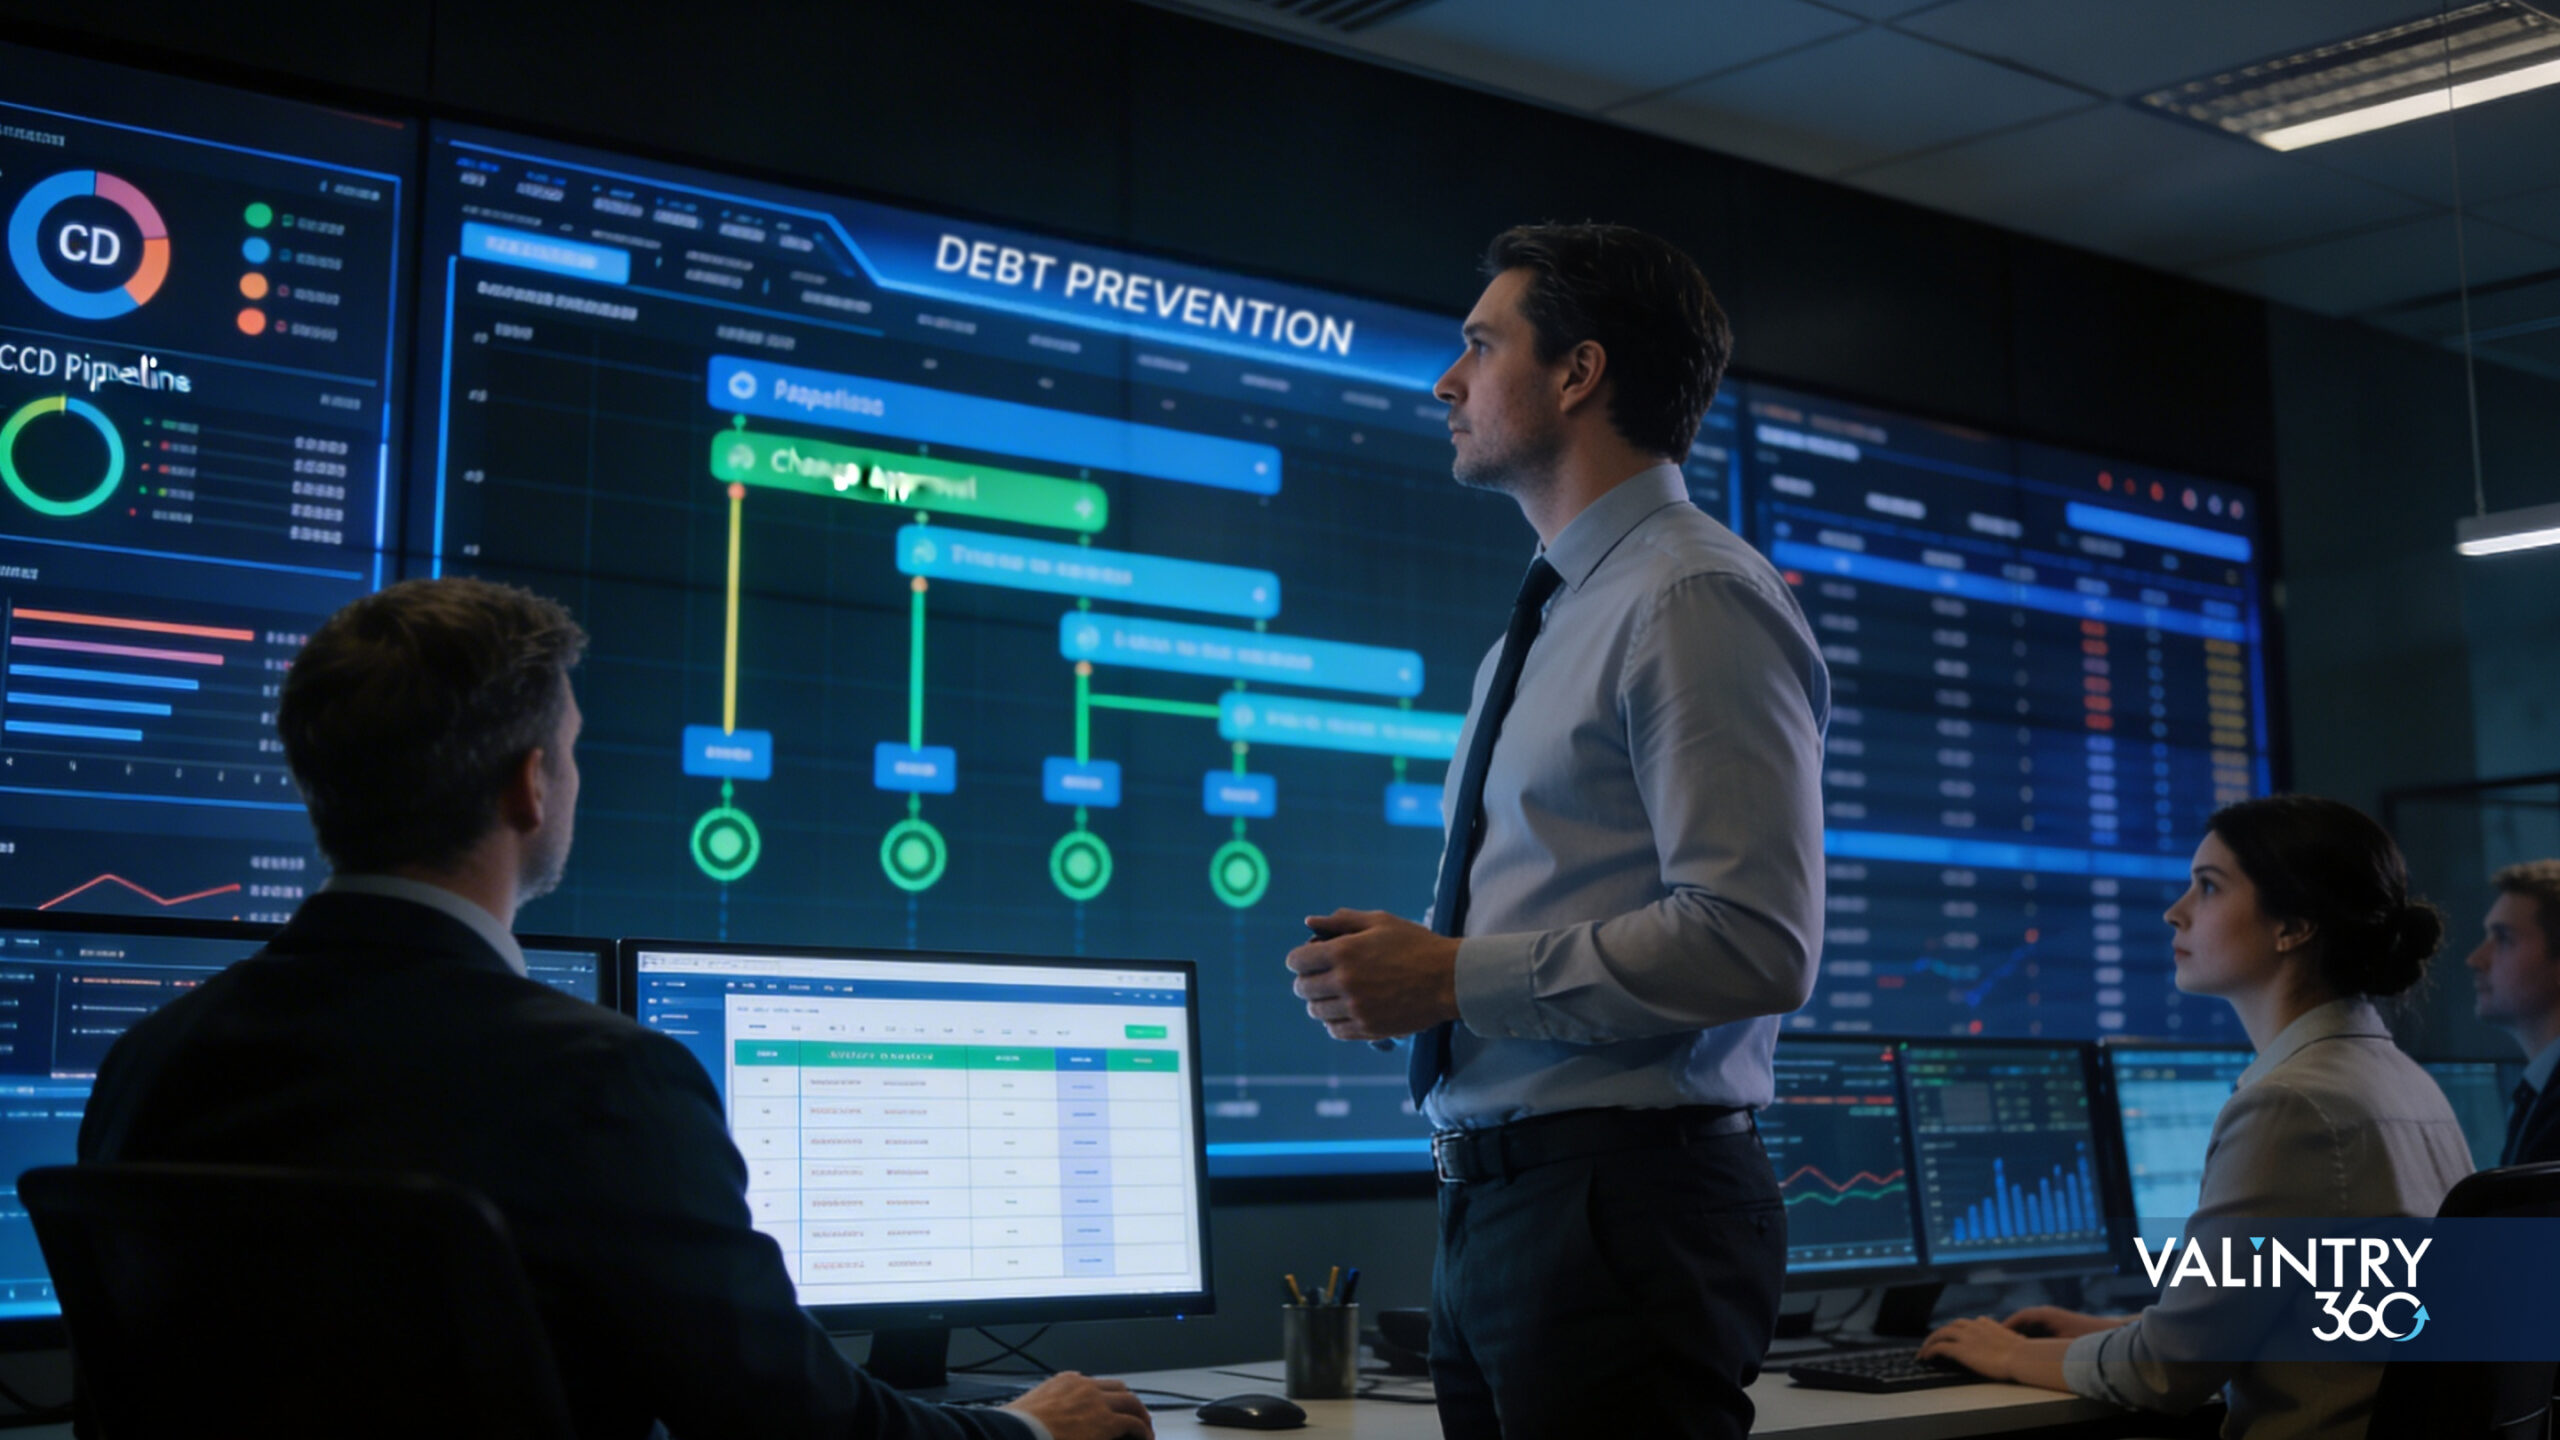
Technical debt doesn’t just appear—it’s released into production. Without disciplined change management, even small updates can introduce breakpoints or vulnerabilities that multiply over time.
Experienced Salesforce Consulting and Solutions partners enforce structured release management that mirrors software engineering best practices:
- Sandbox strategy that mirrors production environments for accurate testing.
- CI/CD pipelines that automate deployments while enforcing version control and rollback capabilities.
- Code and configuration reviews that catch redundant logic or insecure patterns.
- Automated regression testing that validates both admin and developer changes.
- Approval workflows ensuring stakeholder visibility before deployment.
This approach minimizes chaos, reduces rollbacks, and eliminates the “random admin changes in production” syndrome that silently fuels technical debt. Governance doesn’t slow teams—it frees them from firefighting by making quality predictable.
Continuous Org Health and Optimization as a Business Discipline
Even a perfectly designed Salesforce org can drift into inefficiency if left unmonitored. Over time, unused fields, outdated automation, and dormant licenses accumulate—each adding invisible drag to performance and security posture.
Leading Salesforce Consulting and Solutions partners treat org health as a continuous improvement cycle:
- Regular technical debt audits to identify outdated or redundant configurations.
- License and utilization reviews that right-size costs and eliminate waste.
- Automated reports and dashboards that highlight risk indicators like inactive users or untested flows.
- Deprecation of legacy automations to maintain alignment with Salesforce’s evolving platform.
- User training and enablement to prevent the reinvention of outdated processes.
By turning optimization into a routine discipline, organizations keep their Salesforce instance clean, performant, and secure—without major overhauls or costly rework. The result is a platform that evolves as fast as the business does.
Translating Governance Into Real Business Value
Technical discipline isn’t just an IT goal—it’s a strategic advantage. When Salesforce runs cleanly and securely, the business experiences measurable benefits:
- Faster scaling and integration during growth or acquisitions.
- Lower cost of change, since updates don’t require untangling legacy logic.
- Cleaner, more trustworthy pipeline data that drives better decision-making.
- Audit readiness that satisfies internal and external stakeholders with minimal disruption.
- Reduced operational noise for IT teams, who can focus on innovation instead of triage.
This is why mature Salesforce Consulting and Solutions partners, like VALiNTRY360, matter. They’ve already built and refined the governance, architecture, and monitoring playbooks that most organizations spend years developing internally. Partnering with such experts accelerates time to value while minimizing the risks of growth, compliance, and scale.
Conclusion
Technical debt and security incidents are not inevitable—they’re preventable outcomes of structured, well-governed design. Treating Salesforce as critical enterprise infrastructure means embedding scalability, compliance, and quality assurance into every stage of its lifecycle.
Engaging a seasoned Salesforce Consulting and Solutions partner like VALiNTRY360 helps organizations implement those safeguards from the start, transforming Salesforce from a potential liability into a resilient growth engine built for the long term.
Related Posts
- Salesforce Org Optimization & Technical
Top 10 Salesforce Org Optimization & Technical Debt…
Companies are adding AI to Salesforce faster than they're cleaning the systems that AI will depend on. Years of duplicate data, overlapping automation, old Apex, unused metadata, integration workarounds, and accumulated permissions don't disappear the moment an AI layer gets…
- Salesforce Org Optimization & Technical
Salesforce Consulting for CRM Consolidation: When Multiple Orgs…
A Salesforce estate can look healthy at the org level while failing at the seams between orgs. One sales team may update an Account in Org A while a service team works from a different Account in Org B. An…
- Salesforce Org Optimization & Technical
Cutting Salesforce License and Maintenance Costs the Smart…
For many organizations, Salesforce has quietly become one of the most expensive line items in the tech budget. Licenses pile up, renewals arrive before usage is reviewed, and administrative upkeep grows as customizations multiply. Most teams don’t even realize how…